We built Guardian Samurai because MCP servers ship faster than anyone can audit them.
The Model Context Protocol makes it trivial to hand an AI agent a new tool. It doesn't make it easy to know what that tool can actually do, or what an attacker could make it do. Guardian Samurai closes that gap with standard, repeatable scans, tests and live security testing.
Our story
Guardian Samurai started as an internal checklist for reviewing MCP servers before they were connected to production agents. The checklist became a taxonomy, the taxonomy became a scanner, and the scanner became the assessment you see today -- a score, a Level 1-3 rating, and a findings report ranked by severity, all produced from a single scan.
We're a small team that cares more about a correct, well-explained finding than a long report. If a check doesn't tell you something actionable, it doesn't belong in the taxonomy.
Today that work spans two products. Samurai Quality scans and tests your MCP servers from the cloud or your own machine. Samurai Security goes further: an authorized, live attack test that probes your server the way an attacker would, so you find its weak spots first.
Every result, in one place, with a fix attached
Our story ends with actionable findings. Here's what that looks like in the product.
Your dashboard
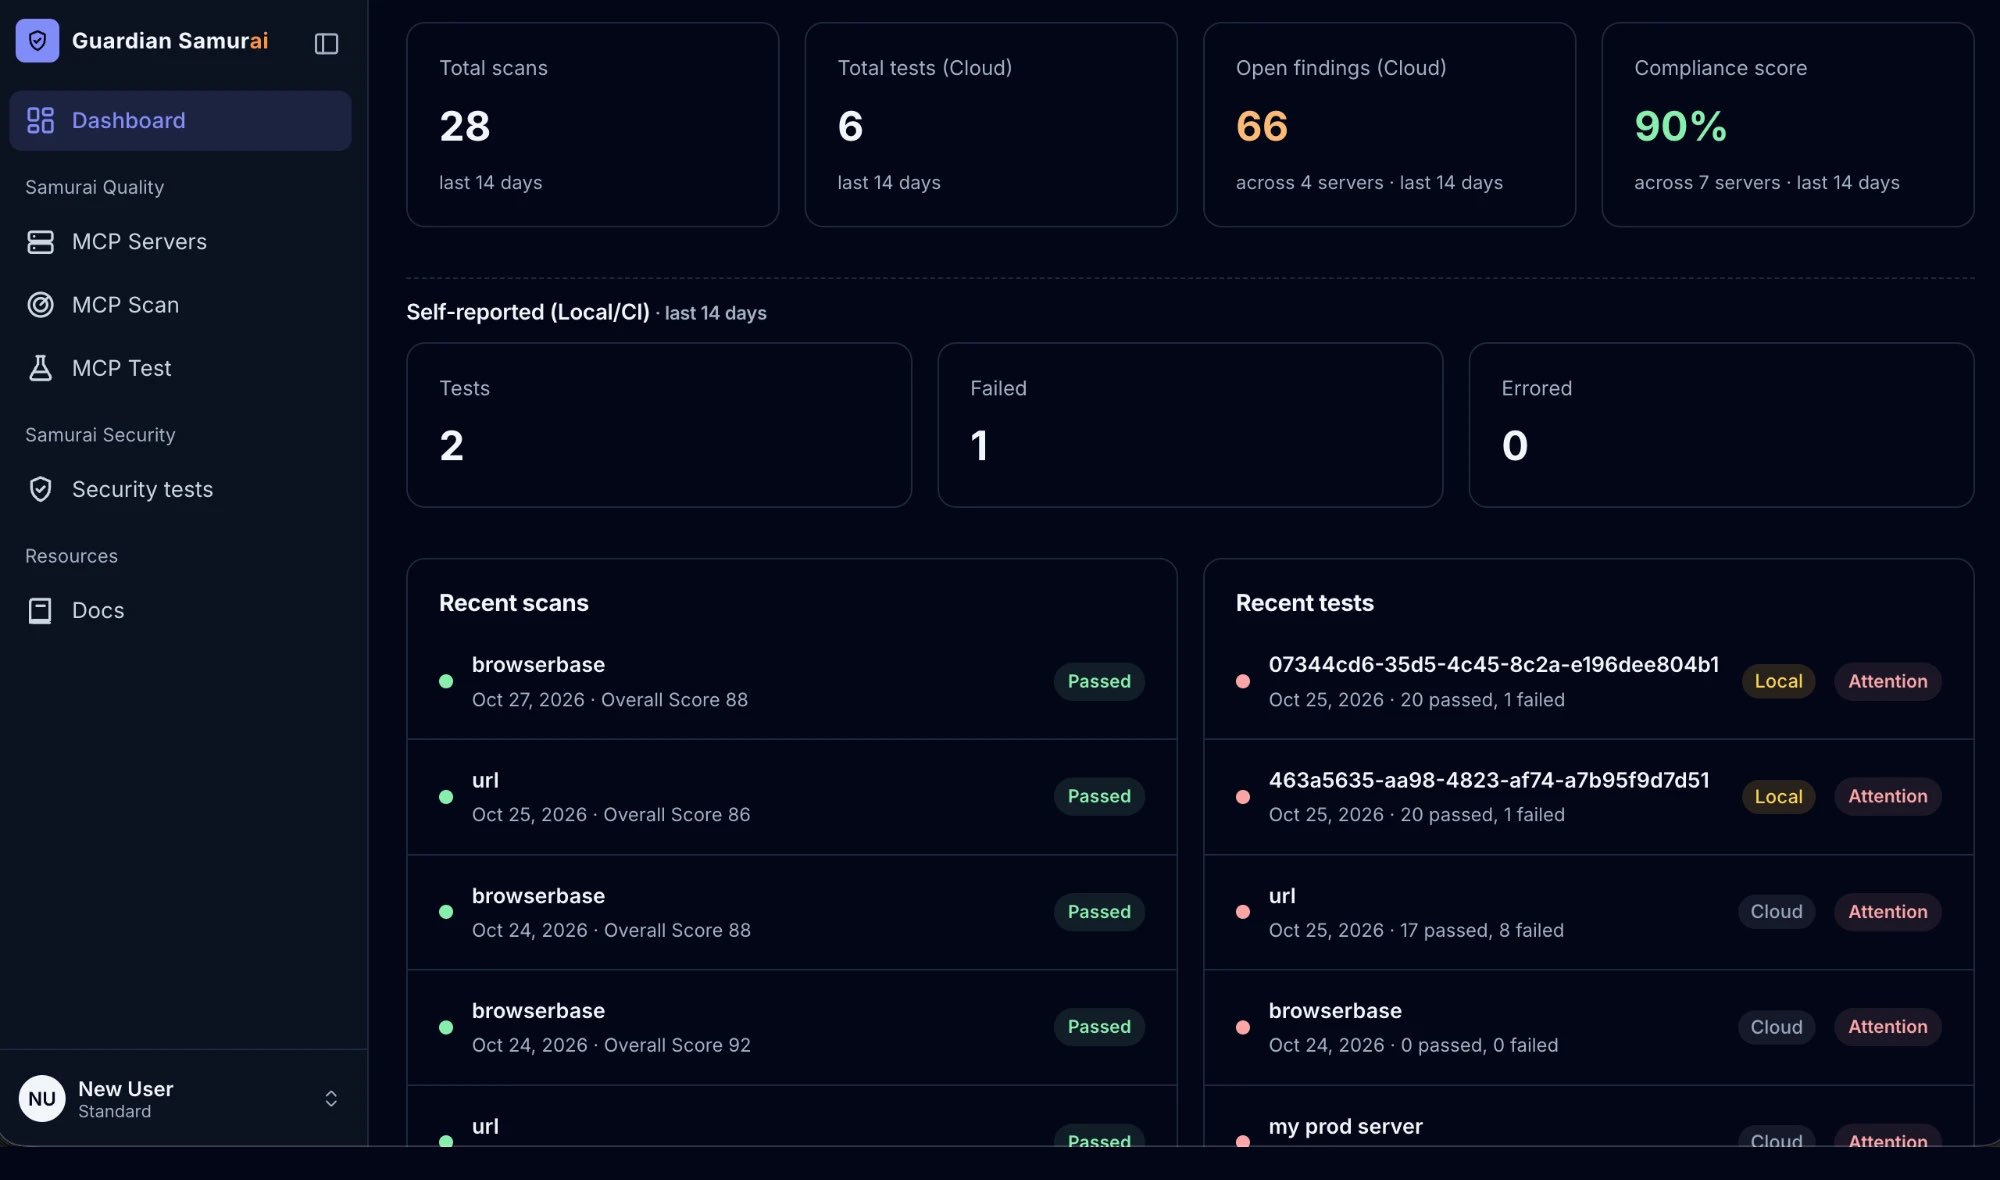
See every scan and test from the last 14 days at a glance, with open findings and your compliance score across all your servers.
- Totals for scans, tests, and open findings
- Compliance score rolled up across servers
- Recent runs with a clear Passed, Review, or Attention status
Your MCP scan score
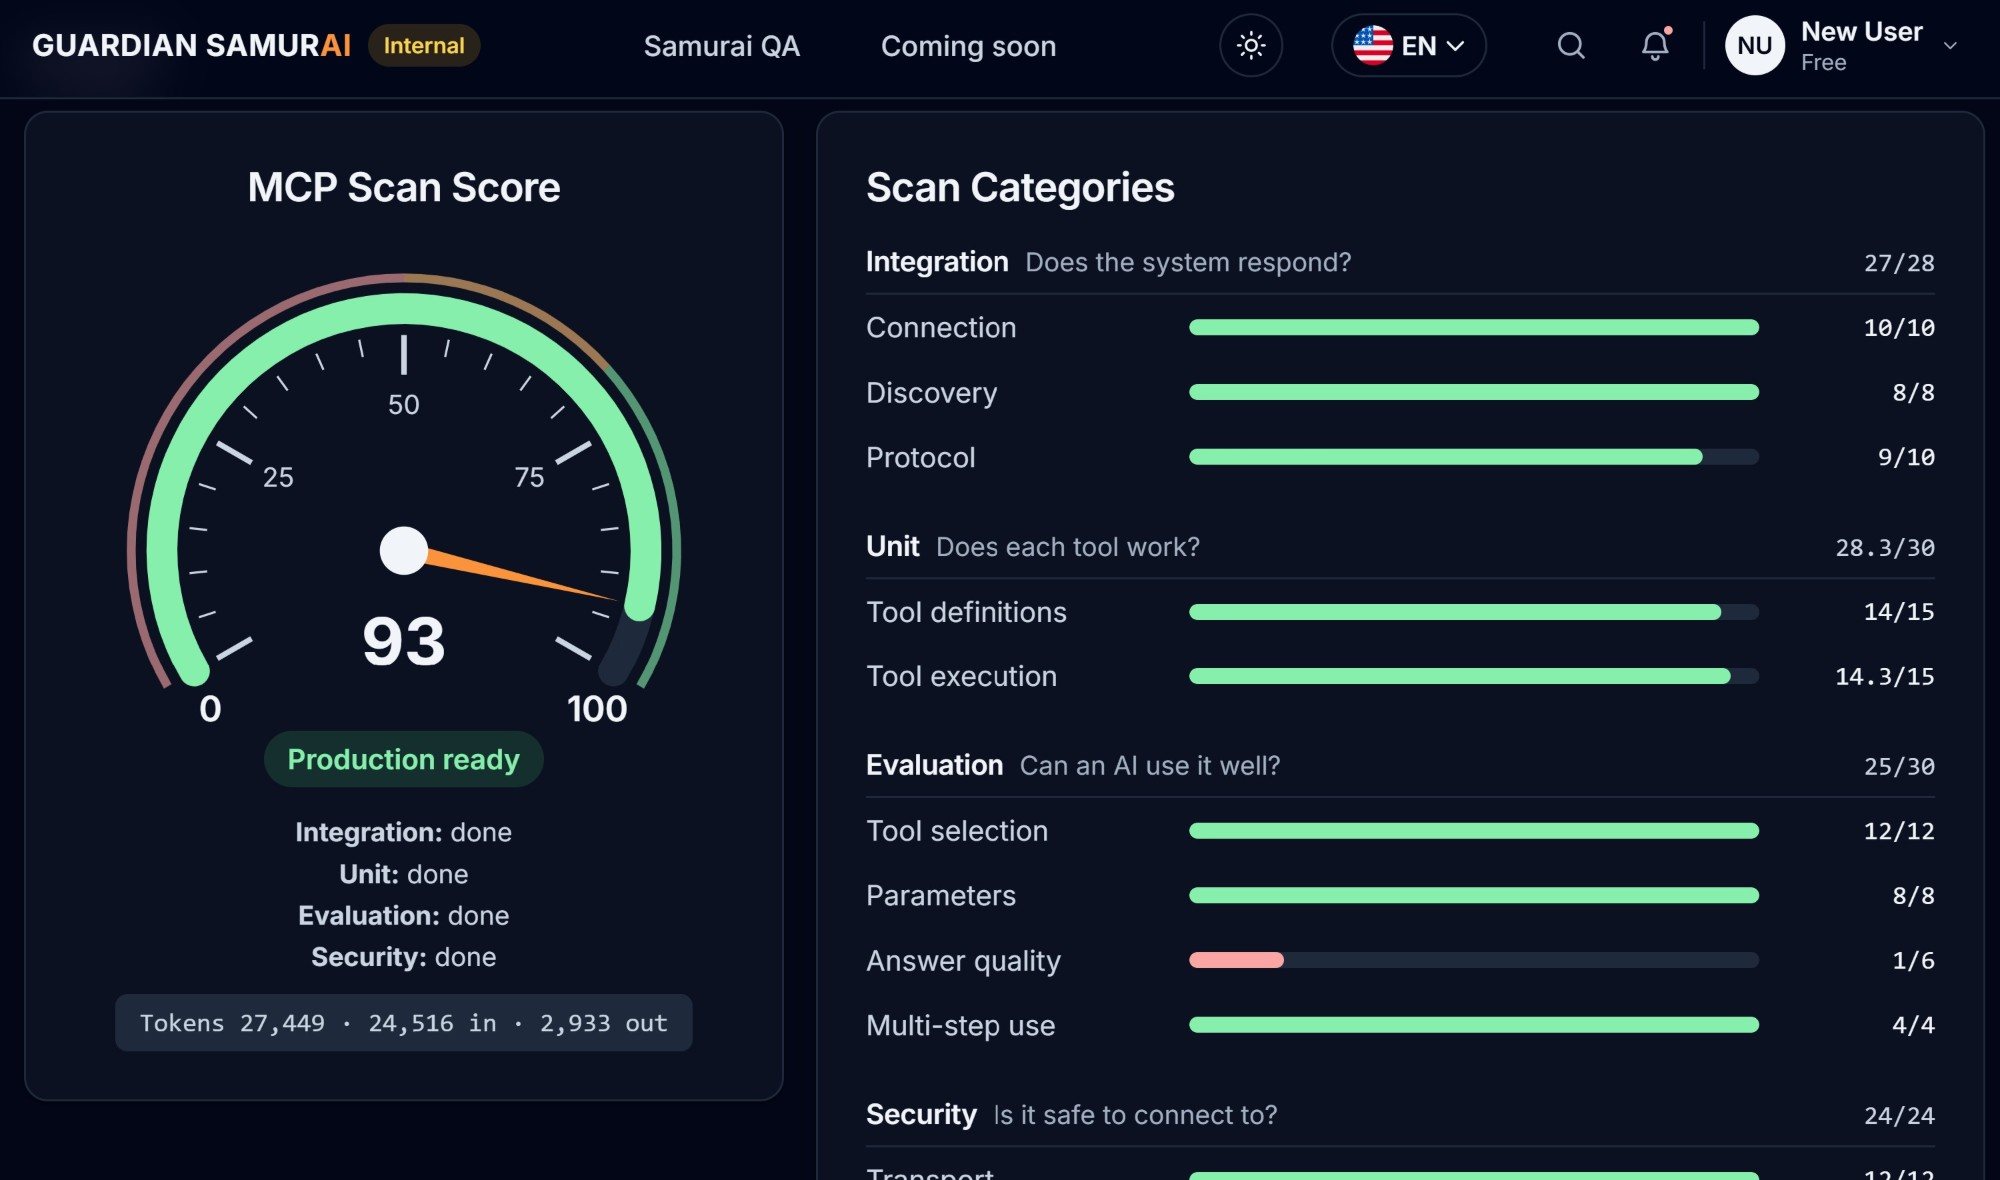
Each scan checks four categories and rolls them into one score out of 100, with a bar for every check so you can see exactly where points were lost.
- Integration: does the system respond?
- Unit: does each tool work?
- Evaluation: can an AI use it well?
- Security: is it safe to connect to?
Actionable findings
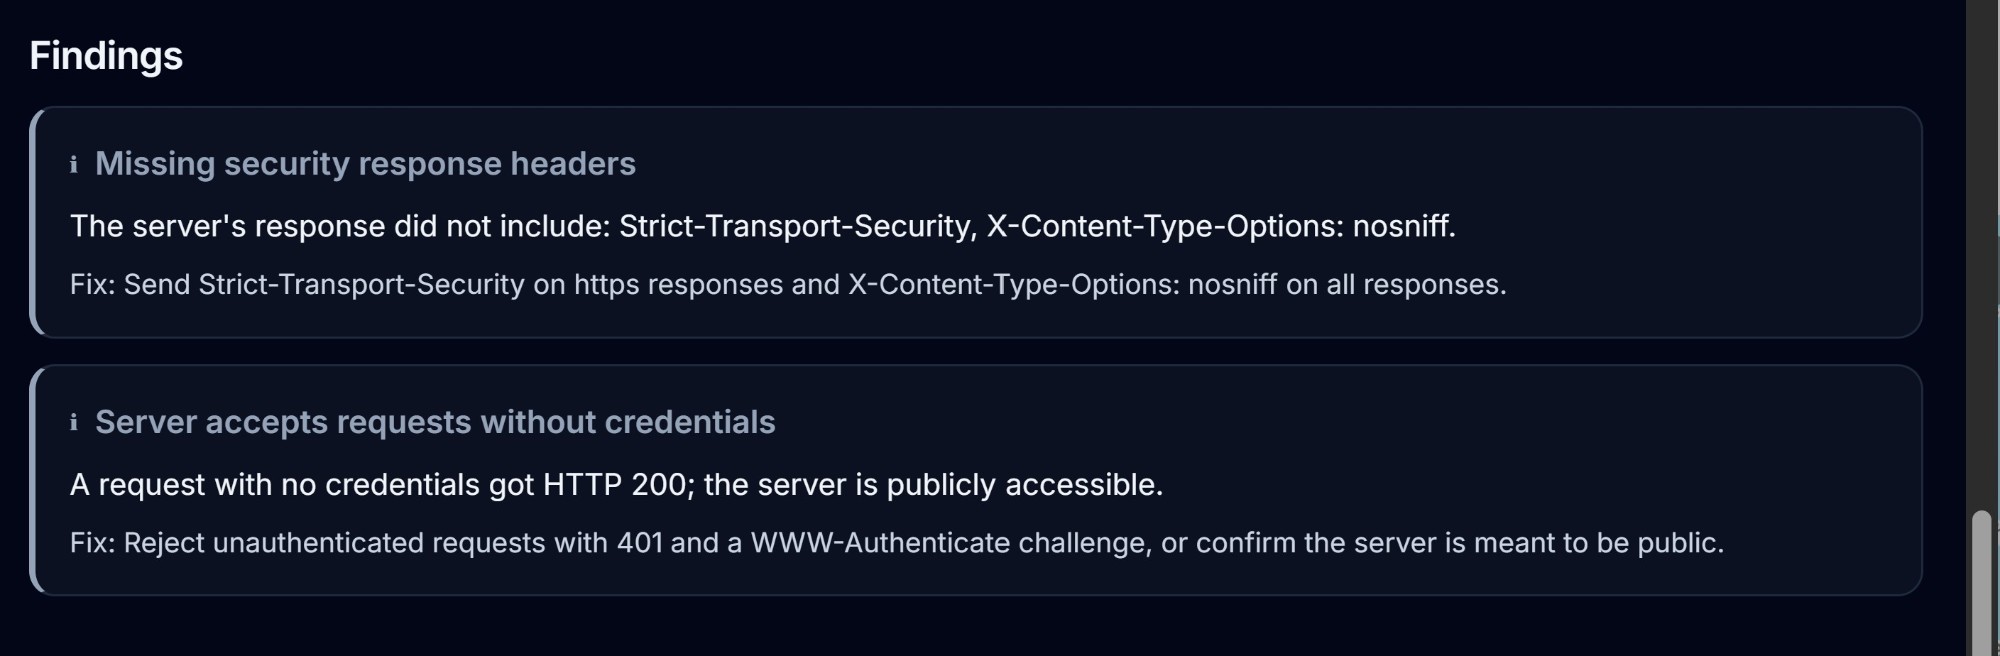
Each finding from a test or scan says what failed, which tool it affects, and the specific change that resolves it.
- Tests: per-tool findings, such as a tool rejecting a valid call
- Scans: server-level findings, such as missing security headers
- Every finding ends with a one-line Fix
Samurai Security
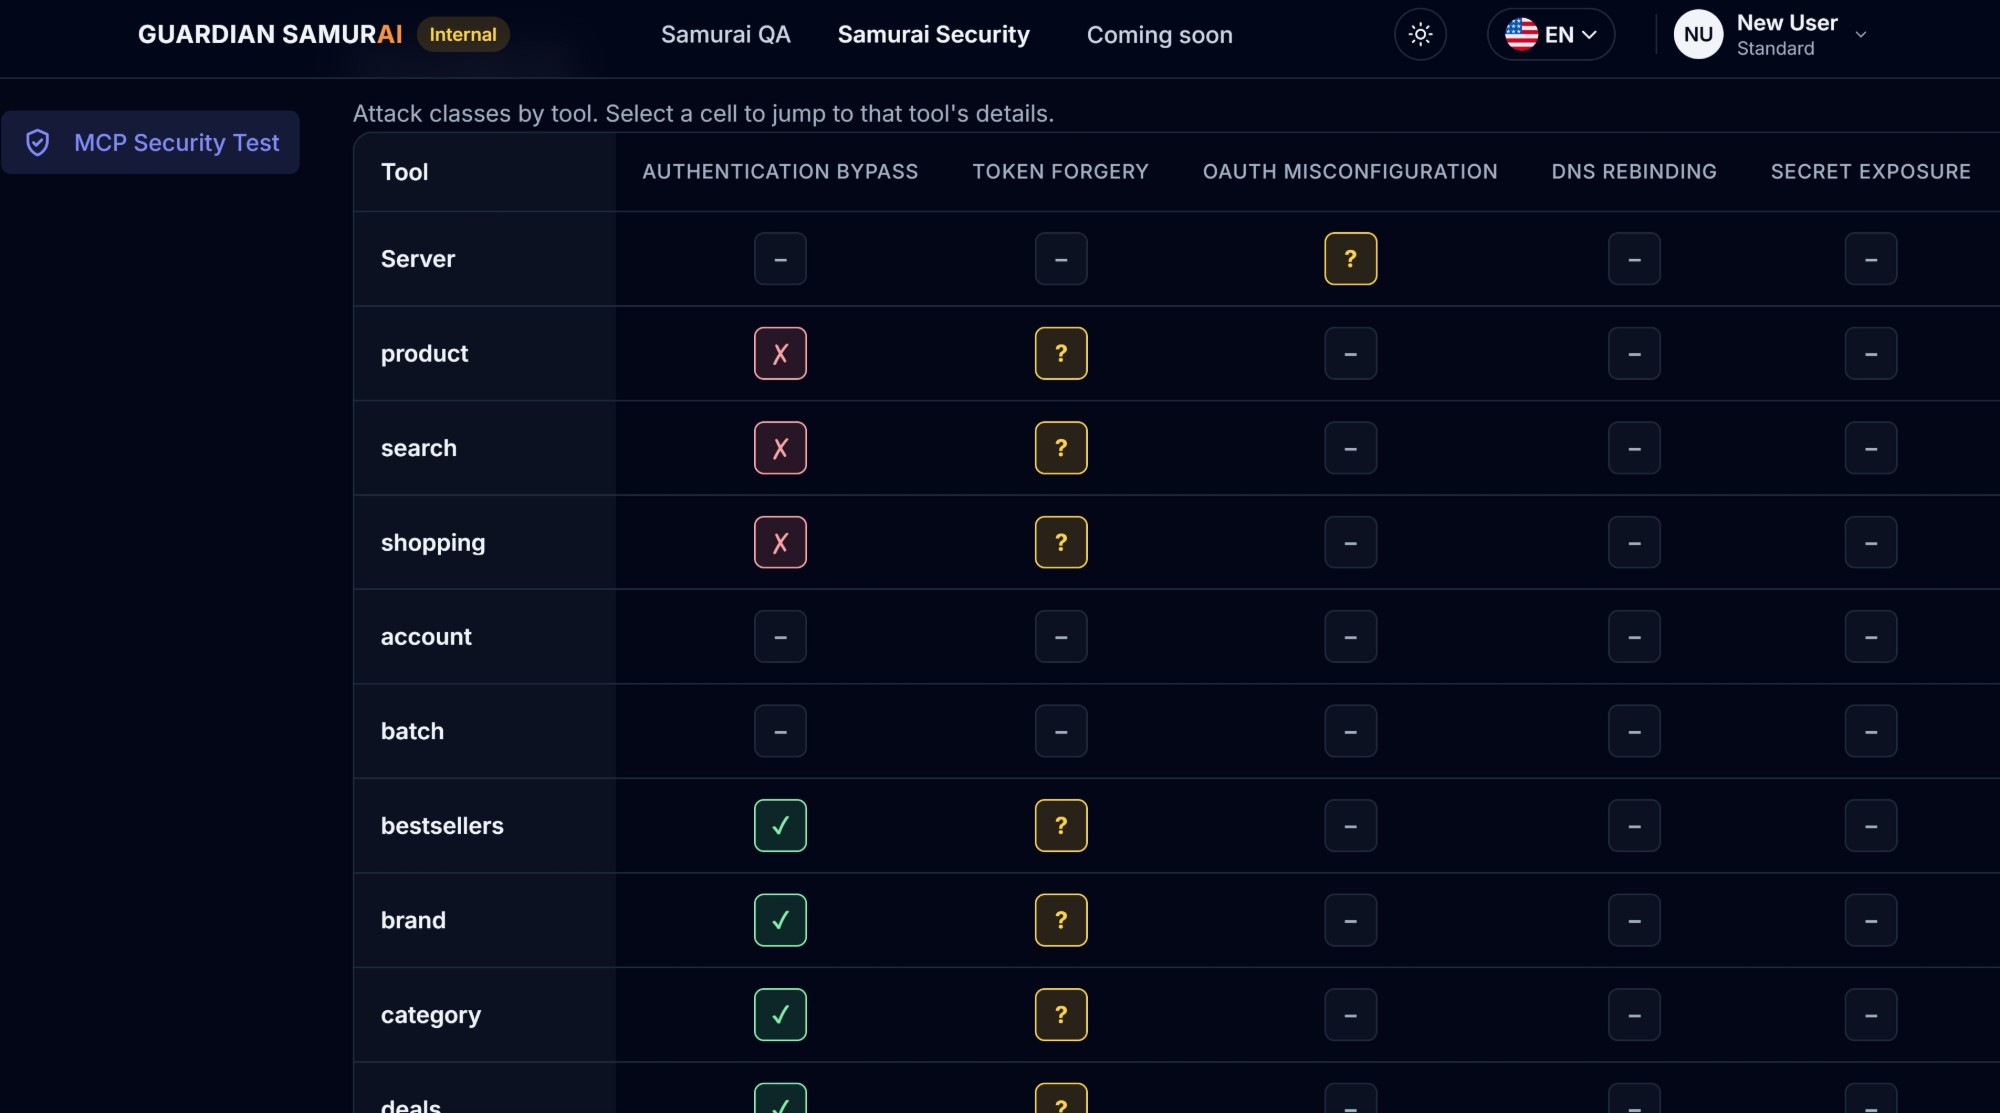
Our newest product runs an authorized live security test against your own MCP server and ends with a matrix of every tool against every attack class.
- Seven attack classes, from authentication bypass to path traversal, in one run
- A reviewable security plan that shows exactly what we send before you run
- Only Admins and Security members can run it; findings come with a suggested fix
What we care about
Transparency over trust-me
A tool having access to your data isn't a finding by itself -- what it does with that access is. We surface behavior, not vibes.
Independent by design
Guardian Samurai scans servers from the outside, the same way an integration would reach them, so results reflect what a real caller sees.
Built for iteration
Security work is never really done. Every scan is kept in history so a server’s posture can be tracked as it changes, not just checked once.